SD-WAN Versus Private MPLS for Property Portfolios
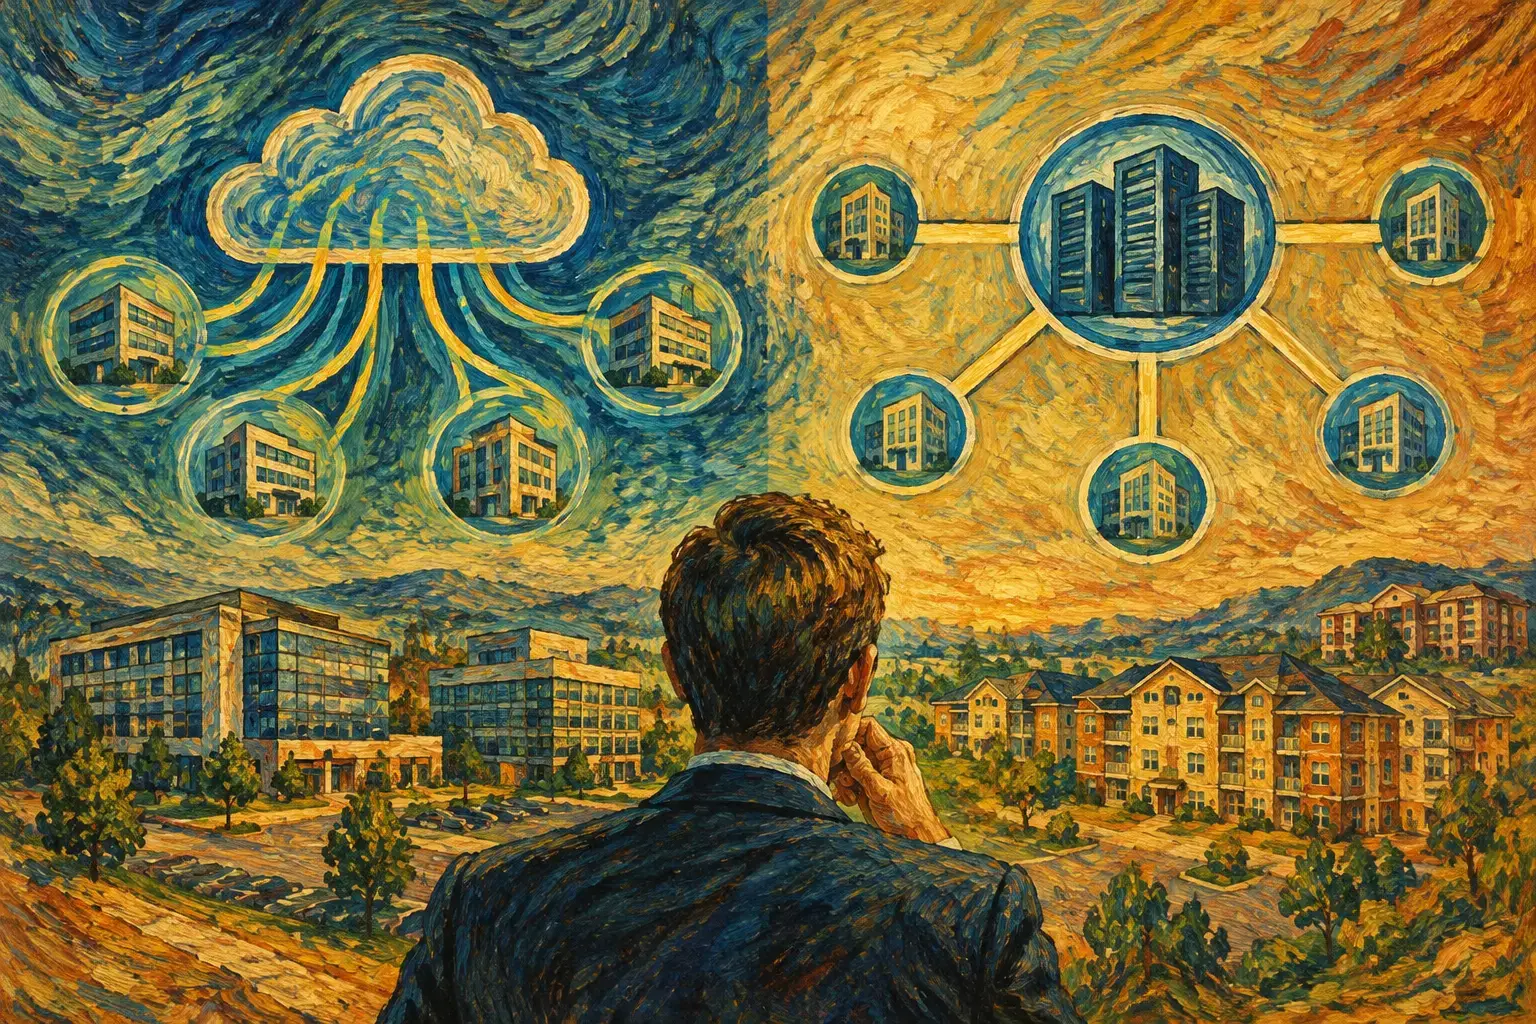
A resident moves in on a Friday, a hotel fills up for a convention, or a senior living community relies on cloud-based clinical applications. In each case, a network outage is not merely an IT ticket. It can disrupt operations, damage the user experience, and create avoidable cost. The SD-WAN versus private MPLS decision matters because it determines how each property reaches the applications and services it depends on.
For portfolio operators, the right answer is rarely a blanket mandate to replace every private circuit or move every location to broadband. It is a business and operational decision shaped by application requirements, local carrier availability, outage tolerance, contract timing, and the cost of supporting a distributed estate.
SD-WAN Versus Private MPLS: The Core Difference
Private MPLS is a carrier-managed private wide-area network. Each site connects through dedicated access circuits, and traffic is carried across the provider’s MPLS network rather than the public internet. For years, MPLS was the standard for connecting branch locations to data centers and centralized applications because it offered predictable routing, defined service levels, and a single carrier accountable for the underlying WAN.
SD-WAN is an overlay technology that manages traffic across one or more connections, which may include business internet, fiber, cable, fixed wireless, LTE, 5G, or even MPLS. It continuously evaluates the available paths and applies policy to route application traffic according to performance, priority, and security requirements.
The distinction is critical: SD-WAN is not simply an internet connection, and MPLS is not automatically obsolete. SD-WAN can use MPLS as one of several available paths. A property may retain MPLS for a critical use case while adding SD-WAN and broadband to improve resilience, visibility, and cost control.
Where Private MPLS Still Makes Sense
MPLS can remain a sound choice when an operation needs highly consistent performance, a defined carrier service-level agreement, and predictable private routing between locations. This can be particularly relevant for centralized voice systems, legacy applications that are sensitive to latency or packet loss, and sites where high-quality broadband options are limited.
Healthcare and senior living operators may also have facilities where operational technology, security systems, clinical workflows, or centralized communications require conservative network design. MPLS does not remove the need for security controls or redundancy, but its controlled network path can simplify certain designs.
The trade-off is flexibility. MPLS bandwidth can be expensive relative to commercial internet access, especially across a large portfolio. Circuit upgrades may require long lead times, and the architecture often backhauls traffic through a central hub even when the application is cloud-based. That can add latency and create dependency on the hub location.
For a property group with dozens or hundreds of sites, another concern is procurement. A legacy MPLS network may be tied to a single national carrier agreement even when that carrier is not the best local provider at every address. The contract may have made sense when it was signed. It may not reflect current access options, pricing, or property needs.
Why SD-WAN Changes the Conversation
SD-WAN gives operators more control over how traffic moves across a portfolio. Instead of treating all traffic the same, policies can prioritize what matters. Voice calls, property-management applications, payment systems, guest services, cloud platforms, cameras, and general internet access can each follow different rules.
If a primary circuit degrades, SD-WAN can move prioritized traffic to a secondary path based on the policy set for that application. This is more useful than a basic failover design that only reacts after a full outage. A circuit that remains technically online but suffers from loss, jitter, or poor latency can be just as disruptive to voice and real-time applications.
For properties using cloud applications, local internet breakout is another practical benefit. Traffic destined for cloud services can go directly to the internet from the property rather than traveling back to a data center first. Done correctly, this can improve application response times and reduce unnecessary WAN traffic.
The financial case often begins with access diversity. A managed SD-WAN design can combine two cost-effective local circuits from different providers instead of relying on one premium private connection. But lower monthly circuit costs should not be the only measure. The design must account for device management, licensing, security services, installation costs, support expectations, and the operational impact of an outage.
The Best Choice Is Often a Hybrid WAN
A hybrid WAN combines MPLS, broadband, and wireless under SD-WAN policy control. This approach is useful when a portfolio cannot or should not replace every private connection at once.
For example, a corporate office or high-dependency community may keep MPLS as a primary or protected path while adding fiber internet as a secondary path. A conventional multifamily property might use dual broadband circuits with 5G backup. A newly acquired asset with an unfavorable circuit contract may use an interim design until renewal or construction timing makes a permanent solution practical.
This flexibility supports staged modernization. Operators can address the highest-cost or highest-risk sites first rather than forcing a disruptive, portfolio-wide cutover. It also creates a clearer path for standardizing network policy while allowing the last-mile access at each property to reflect real local conditions.
Evaluate the Decision by Property Function, Not by Technology Label
The most common planning mistake is comparing MPLS and SD-WAN as if they are interchangeable products with one winner. A better approach starts with how each property operates.
A multifamily community may need separate treatment for leasing operations, staff connectivity, smart-building devices, access control, camera traffic, and resident-facing services. A hotel may prioritize guest WiFi operations, point-of-sale systems, front desk continuity, and back-office applications. A senior living campus may need stricter prioritization for clinical, safety, and communication systems.
Ask practical questions before selecting an architecture:
- Which applications fail first when latency, jitter, or packet loss rises?
- What is the real cost of one hour of connectivity loss at this location?
- Are two physically diverse carrier paths actually available at the property?
- Does the current contract create early termination exposure or restrict upgrades?
- Who monitors performance, handles escalations, and owns the outcome when providers blame one another?
Those questions reveal whether a lower-cost broadband design is appropriate, whether private transport should remain in place, or whether a hybrid model provides the best risk-adjusted result.
Security and Support Cannot Be Afterthoughts
SD-WAN can improve network control, but it does not automatically make a property secure. Internet-based paths require an intentional security architecture. Depending on the environment, that may include next-generation firewall services, secure web controls, segmentation, encrypted tunnels, identity-based access, and continuous monitoring.
Segmentation deserves particular attention in property environments. Resident, guest, staff, payment, IoT, building systems, and security traffic should not share unrestricted access simply because they use the same physical connection. The network should support the operational need to isolate traffic while maintaining clear visibility into performance and incidents.
Support design matters just as much. A property team should not have to determine whether the access carrier, SD-WAN provider, WiFi vendor, firewall provider, or application vendor is responsible during an outage. Define escalation ownership before deployment, including after-hours coverage, replacement hardware procedures, reporting, and performance targets.
Build the Business Case Around Total Portfolio Impact
The strongest SD-WAN versus private MPLS business case combines telecom costs with operational outcomes. Compare current circuit charges, contract terms, bandwidth utilization, recurring outages, application performance, and internal time spent coordinating vendors. Then model the target state site by site.
Do not assume the cheapest access circuit produces the lowest total cost. A low-cost connection with poor construction quality, weak support, or no true backup can cost far more during a major service interruption. Likewise, do not renew expensive MPLS simply because it has always supported the business. Test whether the same or better application performance can be achieved through a properly designed alternative.
Carrier-neutral sourcing is especially valuable for portfolios because available providers, construction costs, and service quality vary by address. A national standard should define outcomes and support expectations, not force every property into the same circuit type from the same carrier.
Before making a broad change, audit the existing WAN, contracts, applications, and carrier options at each location. The objective is not to declare MPLS old or SD-WAN new. It is to give every property the connectivity design it needs to protect operations, control costs, and support the experience residents, guests, patients, and staff expect.